
Give AI current context.
Keep decisions under clear rules.
Define what AI may recommend, prepare or execute for each business process. Datastreams supplies permitted context and applies deterministic rules before a configured action proceeds. Your organisation decides when a person must approve and who remains responsible.
Datastreams supports technical and operational governance. It does not replace organisational accountability, legal assessment or the obligations of an AI provider or deployer.
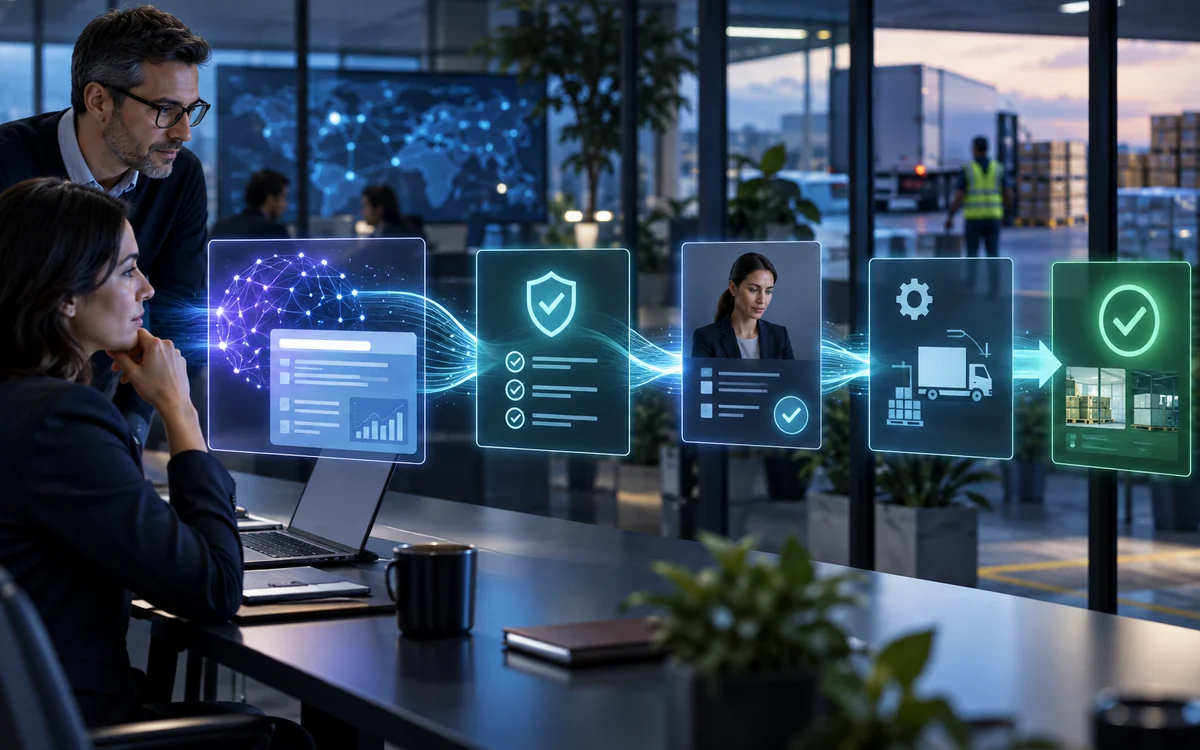
AI inherits the pipeline
A model cannot repair data governance that was never operational.
A static policy cannot constrain a live prompt, tool call or generated action. The permitted context can differ for every person and channel. Before AI participates, the surrounding data service needs explicit quality, purpose, access, provider and execution controls.
Personal data
An AI request can introduce a new purpose, recipient, inference or action. Access must remain tied to an approved task, permitted context and accountable outcome.
Financial and strategic data
Confidential data, forecasts, pricing, transactions and internal decisions require the same explicit authority, provider boundary and traceability.
Operational actions
Risk increases when AI can change state or trigger services. Interpretation should remain separate from permission and execution.
Keep authority outside the model
The model may be replaceable. Business state and authority cannot be disposable.
Agents from different providers can participate without becoming the system of record, receiving unrestricted data access or becoming the final source of operating permission.
Authoritative state
The business keeps its own data, events, objectives and commitments instead of treating model context as permanent memory.
Explicit authority
An agent receives defined data access and permitted actions for a purpose, rather than broad implicit control.
Decision evidence
Relevant input context, configuration, policy result, actor, action and resulting state remain inspectable.
Agent interaction lifecycle
Separate interpretation from authority and execution.
AI suggestions can vary. Permission to act follows explicit, testable rules. For example, an agent may prepare a supplier change while a purchase above the agreed threshold still requires approval.
01
Observe
Supply only the data and context permitted for the task.
02
Propose
Let the model interpret, generate or recommend without silently changing business state.
03
Evaluate
Apply deterministic rules to the proposal, current context and permissions. The same inputs and rule version produce the same permission result.
04
Act
Execute only an allowed action through a controlled application or runtime contract.
05
Record
Retain the outcome and evidence needed for operations, review and improvement.
AI-supported engineering
Make the operation explicit enough for AI to help, without giving AI authority.
AI can help translate business language into a proposed operation, find missing cases and prepare tests. Validation and a responsible approval still determine what may run. OpenAI, Claude, internal models or future systems can therefore change without taking business state or control with them.
See how an operation is preparedbusiness need → AI-assisted proposal → validation → human approval → controlled operation → evidence
AI accelerates description and review. The approved business rules remain authoritative.
Questions the operation must answer
Governance becomes operational when responsibility is testable.
Before an agent receives access, the organisation should be able to answer these questions.
Which objective is the agent helping to maintain?
Which first-party data may it observe, and for which purpose?
Which actions may it propose or execute?
Which policy gate or person can refuse the action?
Which model and configuration version participated?
Which evidence and resulting state must remain?
Regulatory direction
Outsourcing execution does not outsource accountability.
Applicable obligations differ by organisation and use case. The common direction is clear: data quality, third-party dependencies, logging, oversight and control must remain operationally manageable.
AI systems
For high-risk AI systems where the relevant provisions apply, the EU AI Act includes requirements concerning data governance, record-keeping, transparency and human oversight.
EU AI Act on EUR-LexFinancial operations
DORA requires financial entities to manage ICT third-party risk within their own risk framework and states that using third-party ICT services does not remove their responsibility for compliance.
DORA on EUR-LexDatastreams can support the surrounding operating controls without claiming that every AI use case is high-risk, that every organisation falls under DORA or that runtime evidence alone establishes compliance.
Start with one agent action that would matter if it were wrong.
Map the state, purpose, authority, policy gate and evidence before selecting the model.
Map the agent boundary